Our own security posture.
Payers ask about a BAA before the second meeting. Banks ask about SR 11-7. European buyers ask about residency. These are the answers — and the posture behind every agent we ship.
SOC 2 Type II
Independently audited access management, controls and incident response.
Report on requestHIPAA & BAA
PHI stays inside your compliance boundary. Infosec reviews handling before any pilot starts.
BAA capableModel risk
Model cards, validation evidence, drift monitoring and HITL design your MRM function can review.
SR 11-7 · NIST AI RMFData residency & model choice
Your cloud, your region, your models. Vendor neutral, in-VPC deployments.
Multi-cloudFull audit trail
Every prompt, call, output and approval logged, attributable and reversible.
Regulator-readyAdverse decisions stay human
No denial, decline, accusation or termination is ever issued by an agent.
Non-negotiableCitations or it doesn't ship
Every relied-on output carries its source. Unsourced values can't publish or act.
ProvenanceFairness monitoring
Metrics tracked across groups on any agent touching people, thresholds set with compliance.
ContinuousOne-action pause
Your team can stop any agent immediately, with no dependency on us.
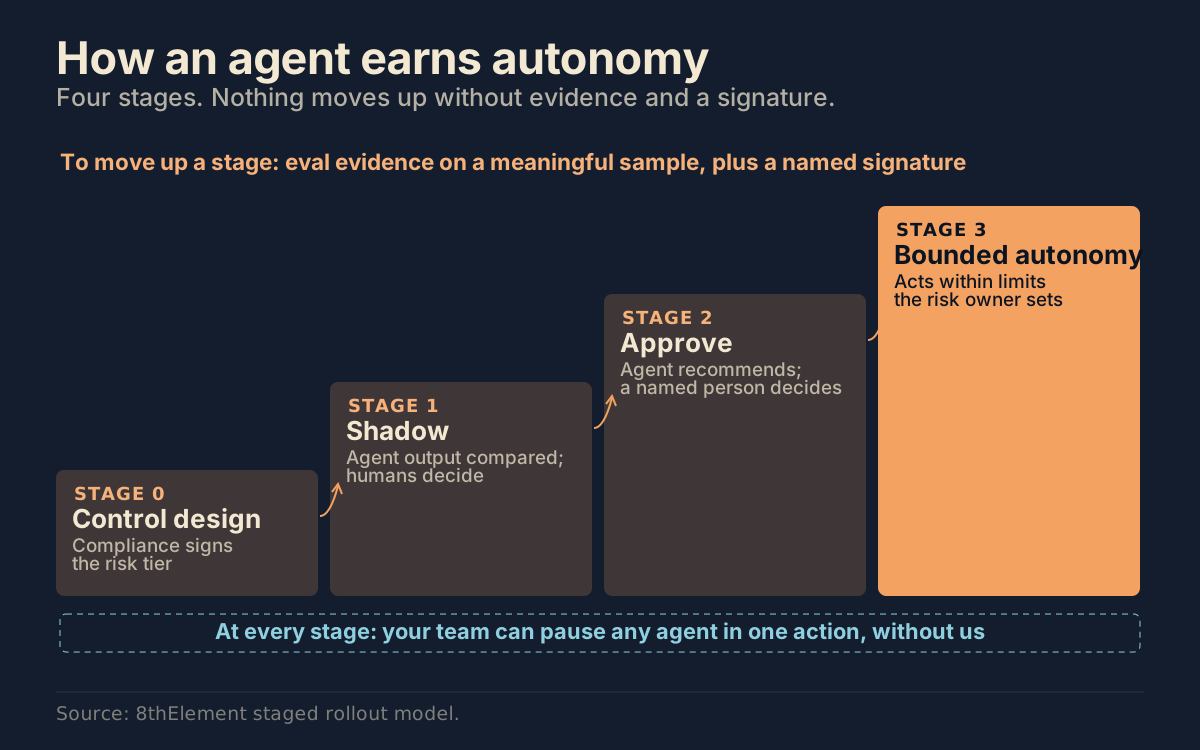
Kill switchHow an agent earns the right to act.
Regulatory exposure and control design
The Regulatory Exposure Mapper lists the regulations and controls each use case needs before approve mode. Compliance signs the risk tier.
Outputs compared, decisions unchanged
The agent produces outputs; humans decide as before. We measure agreement, coverage and failure modes over a meaningful sample.
Recommendations, human signature
A named person approves, edits or rejects each output. Acceptance rate and override reasons are tracked and feed the eval suite.
Acts within thresholds the risk owner sets
Value limits, confidence floors, category scopes, volume caps. Everything outside escalates; severe regression rolls back automatically.
Kill switch and quarterly review
Your team can pause any agent in one action. Thresholds reviewed with compliance every quarter.
What we will send your CISO.
Security questionnaire
SIG or your own template. Turnaround in five business days.
BAA template
Our standard, or redlines on yours.
Architecture & data flow diagrams
Per engagement, showing every place data rests and every model it touches.
Model cards & eval reports
For every agent in production, current within the month.
Penetration test summary
Most recent third party test, under NDA.
A call with our CISO
Before a pilot, not after.